

AI agent fleet likely from Chinese firm Tencent pulled data from rival Alibaba’s maps, researchers say
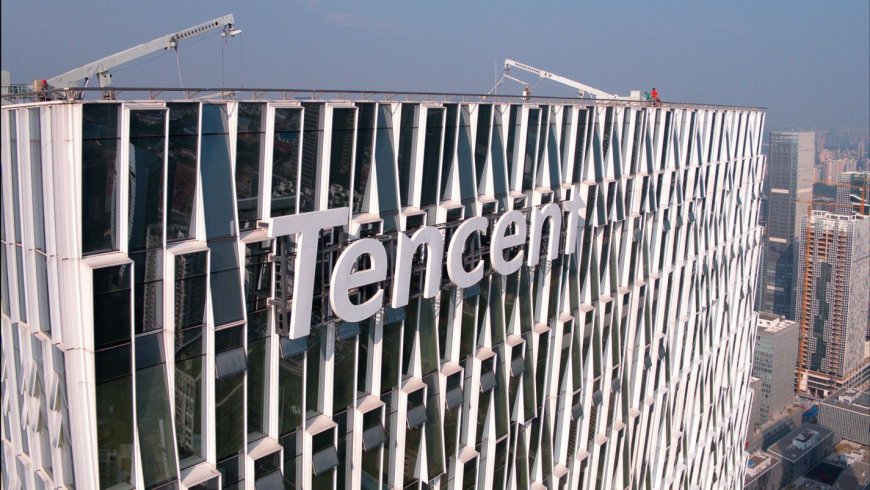
A fleet of AI agents, likely using Tencent’s Hy models, has spent more than a week grabbing data from rival Alibaba’s Amap mapping service, says a preliminary report from the Swarmchasers. The fleet, which ran its code on Tencent Cloud behind a hysandbox-ats proxy, reached a peak of 1,810 URL query scans on Oct. 4 alone. The Swarmchasers, a group of researchers, also noted 211 scans labeled “claude,” a reference to Anthropic’s AI models, though the code behind them matches Chinese models, not Claude.
The free urlquery.net service works by opening a web address in a sandboxed remote browser, with a public record of the scan. It’s used to verify suspicious and risky links and also helps agents reach pages they otherwise would not be able to touch directly. Leveraging the service for this type of agent work is not new, as the nonprofit lab Transluce tied some urlquery activity to OpenAI’s agents last month. The fleet in question this time used similar techniques, but on new targets and infrastructure.
The event timeline began with a single Amap scan on Aug. 25, which the researchers don’t tie to the fleet. The fleet’s own scans started over a month later, on Sept. 28, and peaked on Sunday, with 1,810 of its 2,048 scans through Oct. 4 and 213 of its 216 target locations. That day, from four to eight runs were active at once, with a peak at 14, although that could have been a handful of fast agents, the researchers say. The fleet’s first scan was only three days after OpenAI’s disclosure of it having paused “all training, evaluation, and inference with tool-use” on its most capable models.
The agents sought information about user navigation, discovering what share of Amap users arrive at each entrance of places such as a park, museum, zoo, and hospital, with one location used per run; the researchers found no evidence on urlquery.net that the runs coordinated. At the Chengdu Zoo: North Gate 71%, East Gate 23%, Southeast Gate 6%. A separate place returned: ground car park 40%, main gate 26%, underground car park 11%, plus seven other entrances. The report doesn’t say what the data is for, but speculates that the pattern may be “an evaluation or task-generation run.”
To get around Amap’s protections, the agents relied on the generation of Alibaba anti-bot tokens and the borrowing of public API access keys, in addition to the routing. They also loaded Alibaba’s own Baxia anti-bot scripts, ran an agent-written Puppeteer function through the microlink API, and tried Baidu Translate’s page translator. The method of agent access suggests an intent to bypass the rules.
The agents’ programs sent their results to inboxes on webhook.site, whose public API shows the IP address and software that created each inbox, according to its open-source code. The researchers determined that 15 out of 16 readable Amap inboxes, from Oct. 4–5, were created from Tencent Cloud, 13 of them by a script rather than a person. The 16th came from Iraq and looked like a person rather than the fleet, the researchers said.
Nine requests from the agents’ own code reached the inboxes from Tencent Cloud in Hong Kong, each carrying a Via header ending “(hysandbox-ats).” A forwarding proxy will add that header to name itself, in this case Apache Traffic Server, under a name chosen by whoever runs it, so the report treats that name as self-reported. One marked request, for Ta’er Temple, only took one second to hit after the inbox was created, 35 seconds before its address appeared anywhere public, so only the environment that created the inbox could have known it.
The “HY” identifier suggests Tencent’s Hunyuan models, although no public documentation of hysandbox exists. Tencent holds a security certificate for hysandbox.tencent-cloud.com addresses, but those names resolve to Tencent Cloud Beijing. That is not the fleet’s network, and nothing ties them directly to the proxy. Tests run by a separate team but not reviewed by the researchers suggest that the fleet did not run in Tencent Cloud’s public Agent Sandbox service in its standard internet mode. The report also cautions that “Tencent Cloud is open to anyone.”
The “claude” label appeared on 211 of the 2,048 scans through Oct. 4. Although this suggests use of Anthropic’s models, one classifier came back with a 0% reading for Claude and a second also ranked Hy4 first. In the researchers’ tests, Claude models never put their own name in a tag, while Tencent’s Hy3 called itself Claude in 29 of 36 answers when asked: “Which AI model are you, and which company trained you?” The report, which cautions that those model tests are small, says “the fleet is almost certainly not Claude.”
As it stands, no comment is currently on record from either Tencent or Alibaba. The fleet apparently hasn’t stopped, either: an update to the report says that the Oct. 5 pause lasted about eight hours and that the fleet continued to run that night. On its return, its programs reported to the same inbox as before the pause. A third party had left a note there that cited the report, with instructions for the operator to rotate its infrastructure. The researchers say “a full report will follow,” with no date given.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Angry
0
 Sad
0
 Wow
0